Why line count is a broken proxy for pull request risk
Traditional engineering metrics measure pull request size by lines added and deleted. In practice, production outages almost always stem from small, subtle modifications to connection pools, retry loops, authentication guards, or schema migrations.
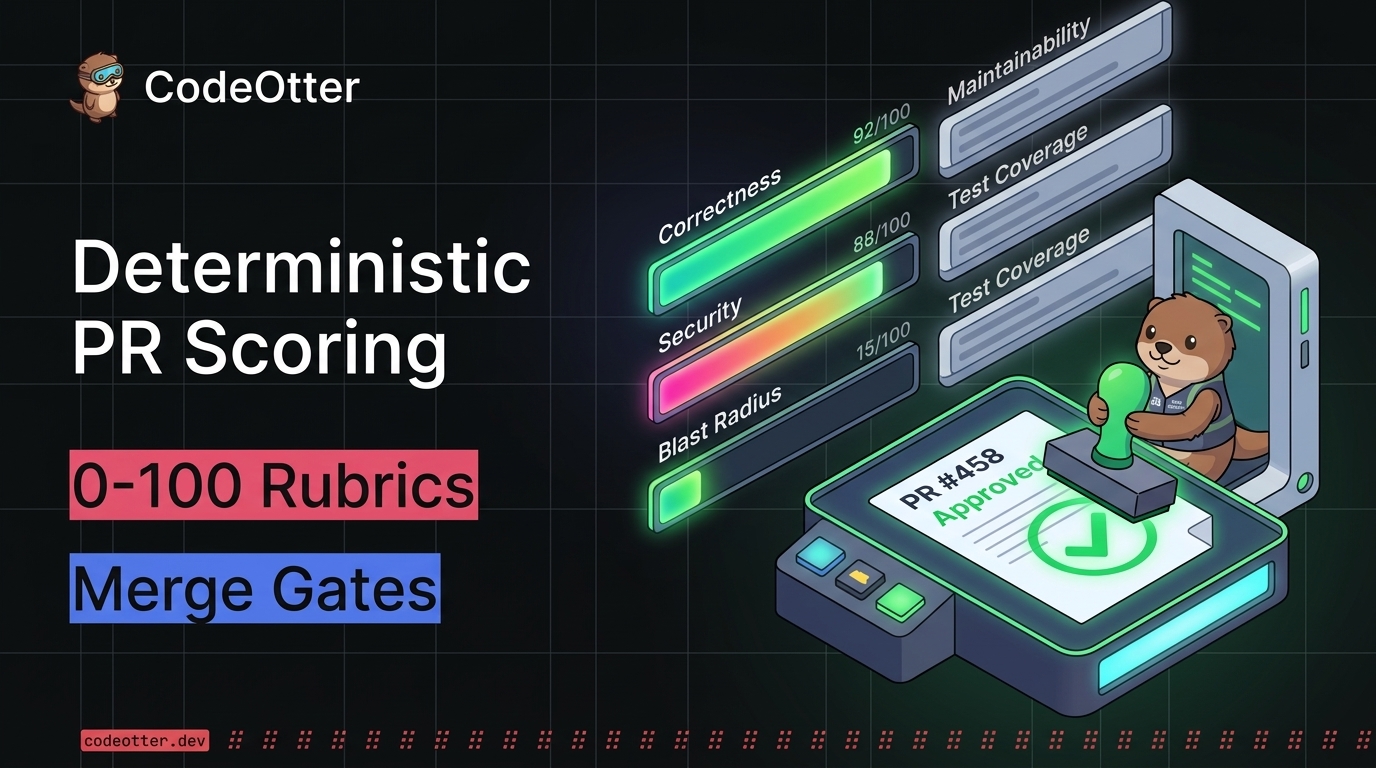
CodeOtter evaluates Blast Radius as an explicit System One gauge alongside Quality, Risk, Tests, Readability, and PR Hygiene—identifying when a modified function sits on a critical cross-service path.
Automated security rubrics and strict input validation
Alongside the 0–100 Security score, CodeOtter runs binary S1_GATES checks for hardcoded credentials, missing authorization guards, and unsafe shell or SQL interpolation—following the same strict validation rules (OWNER_RE, REPO_RE, PR_URL_RE) enforced inside CodeOtter's own backend.